Fuzzing Techniques Overview
Fuzzing remains a cornerstone in the realm of software testing and security research. By automating the discovery of vulnerabilities, it empowers developers to build more robust and secure applications.


Identify security flaws before attackers do, automatically and at scale with Penzzer's intelligent fuzzing engine.

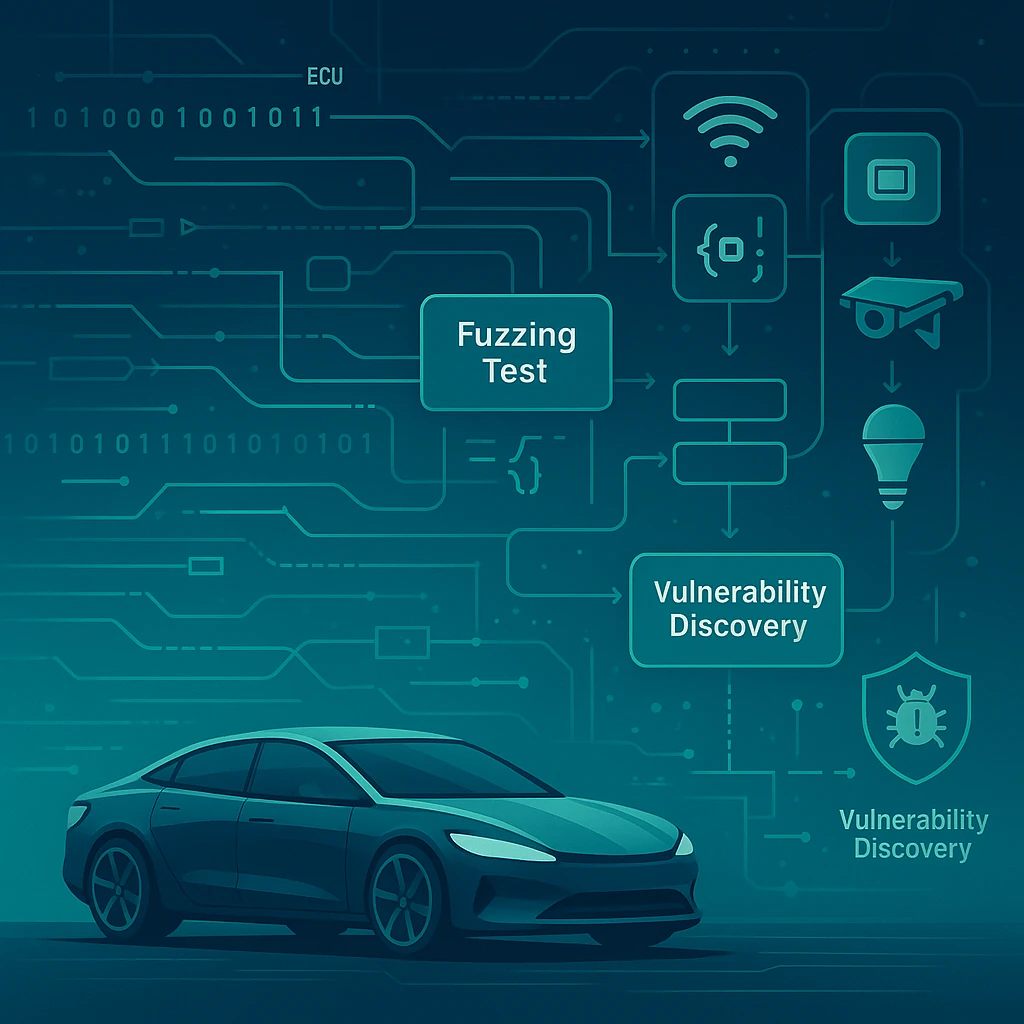
Unified Automotive and IoT Security Testing Tool
Accelerate Vulnerability Detection with Pen Testing and Dynamic Fuzzing
Find and fix vulnerabilities fast, only Penzzer unifies pen testing and dynamic fuzzing to meet compliance standards
Uncover hidden vulnerabilities in your IoT/automotive systems 5x faster than manual testing.